#13Multiple Choice
A security engineer is designing an IAM policy to protect AWS API operations. The policy must enforce multi-factor authentication (MFA) for IAM users to access certain services in the AWS production account. Each session must remain valid for only 2 hours. The current version of the IAM policy is as follows: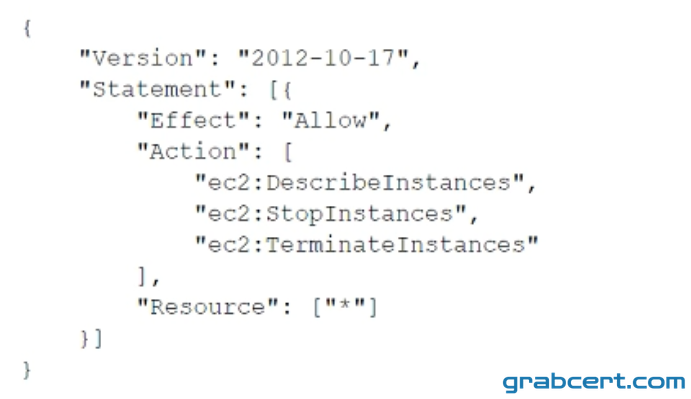
Which combination of conditions must the security engineer add to the IAM policy to meet these requirements? (Choose two.)
Question 13 of 307
Exam AWS-CERTIFIED-SECURITY---SPECIALTY-SCS-C02 Topic 1 Question 13
Back to all questions