Back to Exams
AmazonSCS-C03
AWS Certified Security - Specialty
This certification validates practical cybersecurity skills in cloud architecture and operations, including protecting systems, investigating threats, and applying effective controls. It is intended for professionals who assess risk and respond to real-world security scenarios.
Rate this exam
Exam Details
Total Questions
85Last Updated
Aug. 2026Rating
4.7
Question Types
Multi choices
78Hotspot
7 Get Full Access
Unlimited access to all questions
Detailed explanations for every question
Page progress: 1 / 176%
#1Multiple Choice
A security engineer is troubleshooting an AWS Lambda function that is named MyLambdaFunction. The function is encountering an error when the function attempts to read the objects in an Amazon S3 bucket that is named DOC-EXAMPLE-BUCKET. The S3 bucket has the following bucket policy: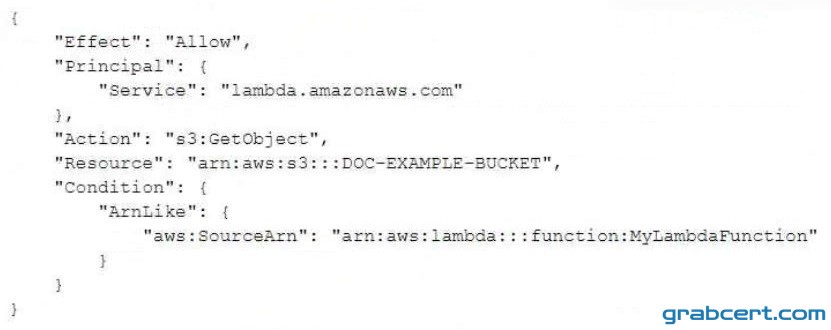
Which change should the security engineer make to the policy to ensure that the Lambda function can read the bucket objects?
#2Hotspot
HOTSPOT -
A company is building a web application that needs to authenticate external users across multiple microservices that the company hosts on Amazon Elastic Container Service (Amazon ECS). The solution must use temporary credentials and minimize the management overhead required to maintain user databases.
Select and order the correct steps from the following list to implement a secure authentication strategy that meets these requirements. Select each step one time or not at all.
Configure Amazon Cognito user pools for user authentication.
Set up an IAM role for each microservice. Grant each role appropriate permissions.
Implement an Amazon API Gateway HTTP API with AWS Lambda authorizers to validate tokens before forwarding requests to microservices.
Create an Amazon DynamoDB table to store user credentials for each microservice.
Create an Amazon Cognito application client to interact with the web application.
Set up AWS IAM Identity Center to give users access to the microservices.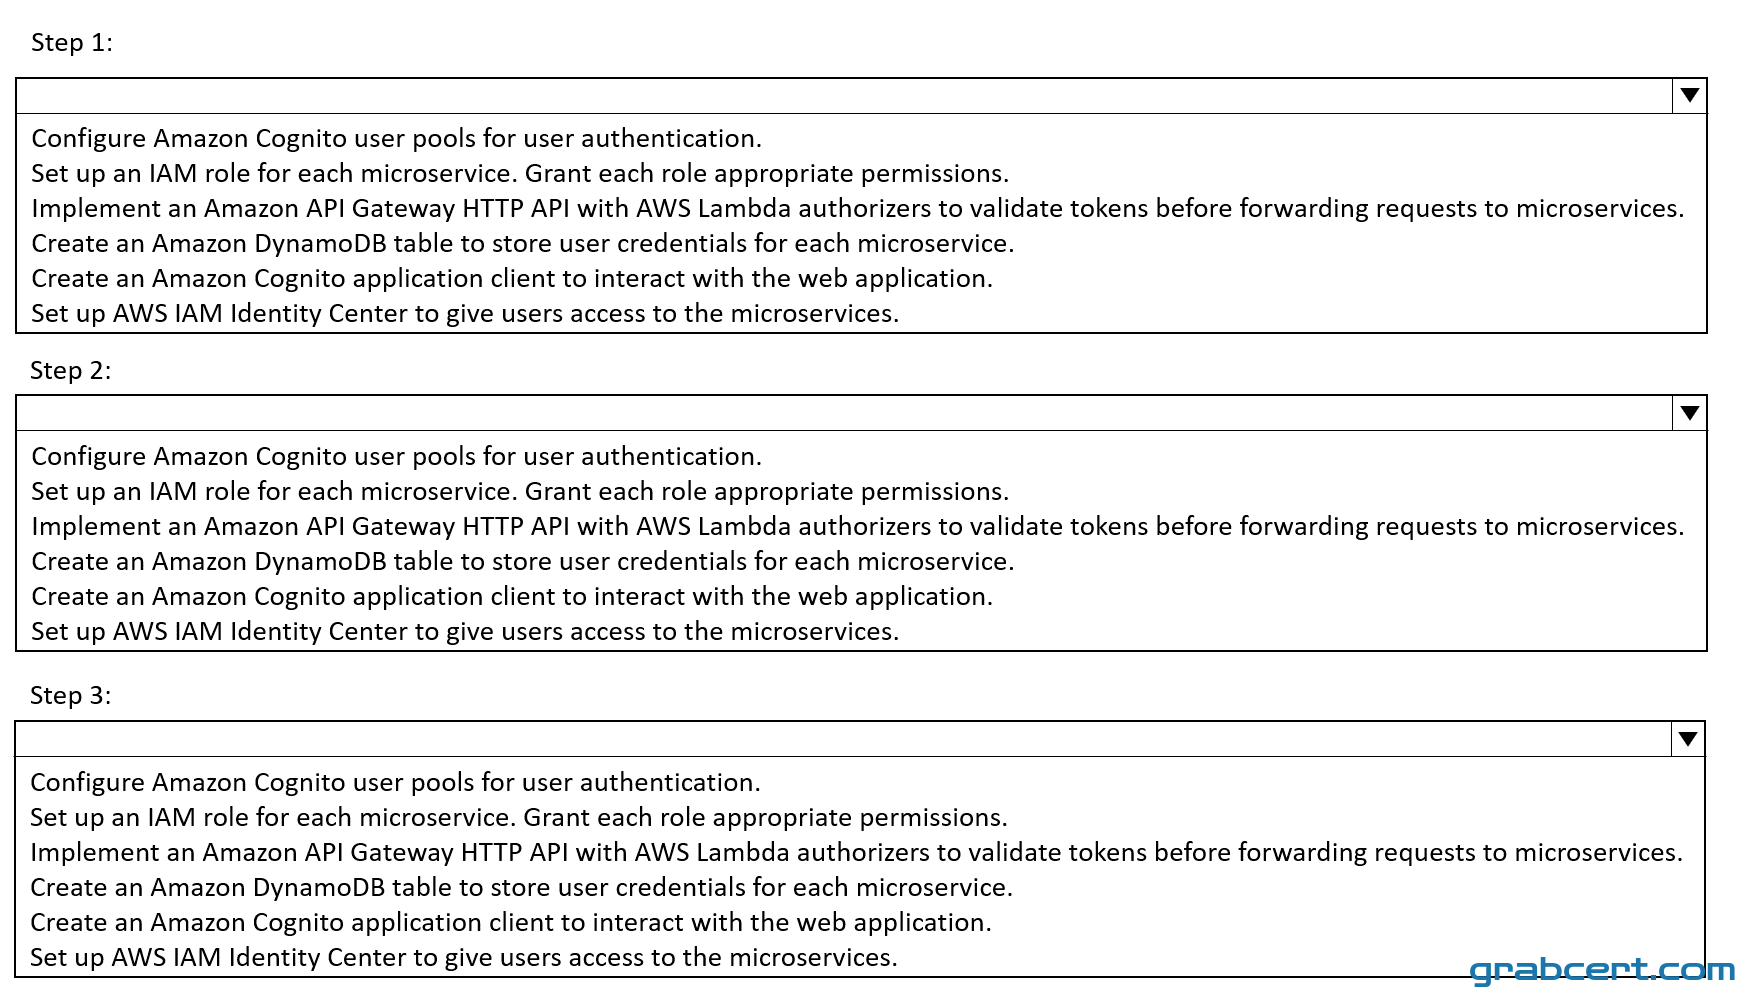
#3Multiple Choice
An AWS account administrator created an IAM group and applied the following managed policy to require that each individual user authenticate using multi-factor authentication: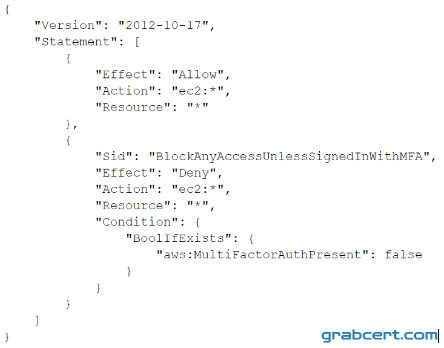
After implementing the policy, the administrator receives reports that users are unable to perform Amazon EC2 commands using the AWS CLI.
What should the administrator do to resolve this problem while still enforcing multi-factor authentication?
#4Multiple Choice
A company is using AWS Organizations with the default SCP. The company needs to restrict AWS usage for all AWS accounts that are in a specific OU.
Except for some desired global services, the AWS usage must occur only in the eu-west-1 Region for all accounts in the OU. A security engineer must create an SCP that applies the restriction to existing accounts and any new accounts in the OU.
Which SCP will meet these requirements?
#5Hotspot
HOTSPOT -
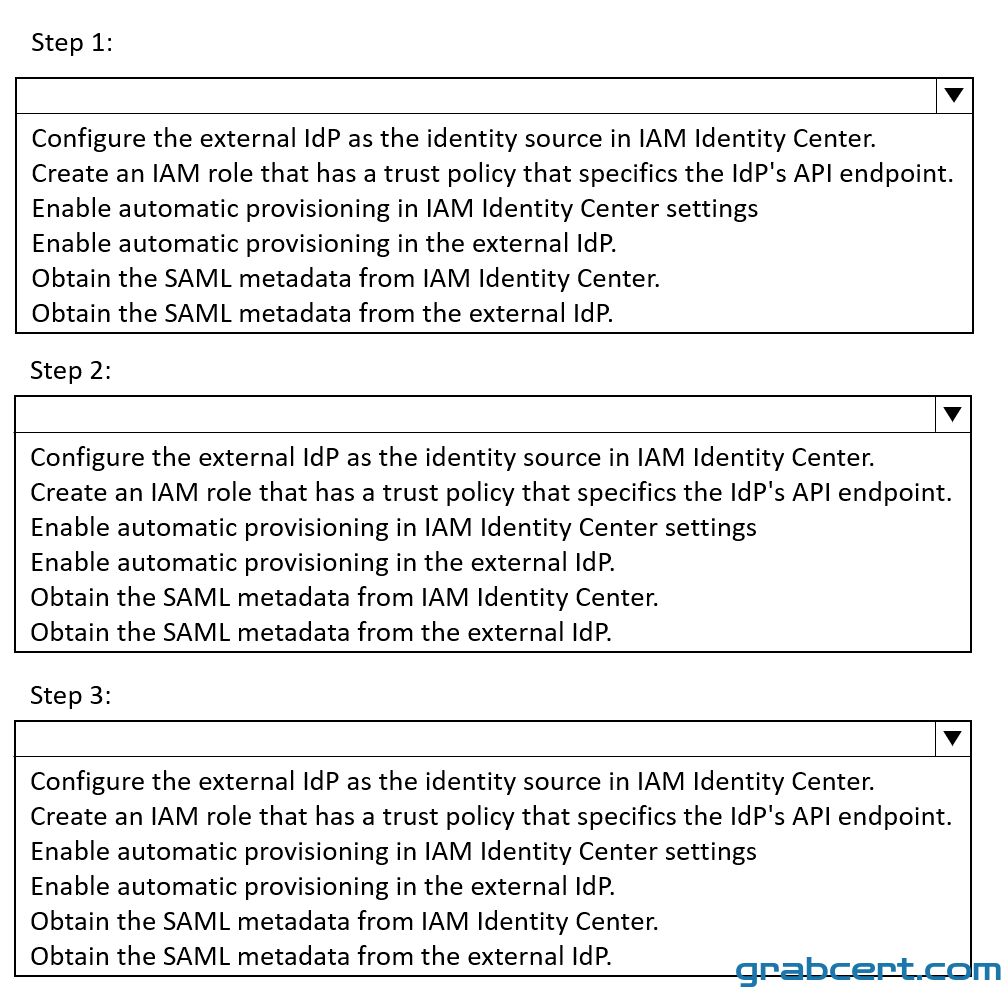
A security engineer needs to implement AWS IAM Identity Center with an exlemai identity provider (IdP).
Select and order the correct steps from the following list to meet this requirement. Select each step one time or not at all.
Configure the external IdP as the identity source in IAM Identity Center.
Create an IAM role that has a trust policy that specifics the IdP's API endpoint.
Enable automatic provisioning in IAM Identity Center settings
Enable automatic provisioning in the external IdP.
Obtain the SAML metadata from IAM Identity Center.
Obtain the SAML metadata from the external IdP.