GrabCert
HomeExamsProvidersAbout
Sign InSign Up
Home/Exams/Cisco Conducting Forensic Analysis and Incident Response Using Cisco CyberOps Technologies (CBRFIR)/Question #4
#4Multiple Choice


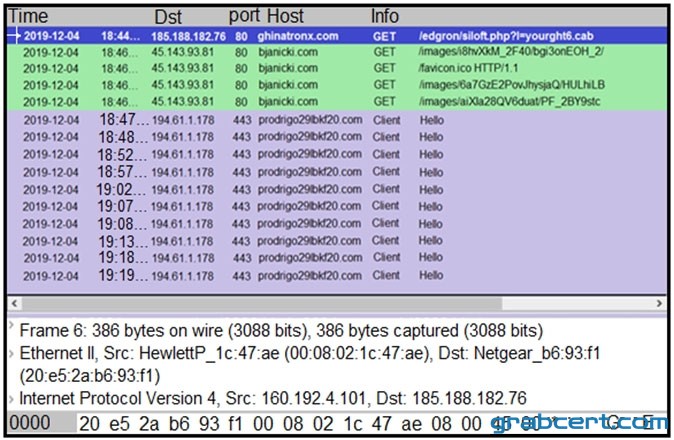
Refer to the exhibit. A network engineer is analyzing a Wireshark file to determine the HTTP request that caused the initial Ursnif banking Trojan binary to download. Which filter did the engineer apply to sort the Wireshark traffic logs?

Previous
Question 4 of 134
Exam 300-215 Topic 1 Question 4
Back to all questions
Next
GrabCert

Your trusted source for certification exam preparation. Pass your exams with confidence.

Quick Links

  • Home
  • Exams
  • Providers

Legal

  • About
  • Contact Us
  • Refund Policy
  • Privacy Policy
  • Terms of Service

© 2026 GrabCert. All rights reserved.

Sign InSign Up