Back to Exams
Cisco350-201
Performing CyberOps Using Core Security Technologies (CBRCOR)
This certification validates practical cybersecurity skills in security operations and risk control, including protecting systems, investigating threats, and applying effective controls. It is intended for professionals who assess risk and respond to real-world security scenarios.
Rate this exam
Exam Details
Total Questions
228Last Updated
Aug. 2026Rating
4.7
Question Types
Multi choices
214Drag&Drop
14 Get Full Access
Unlimited access to all questions
Detailed explanations for every question
Page progress: 2 / 464%
#6Multiple Choice
The physical security department received a report that an unauthorized person followed an authorized individual to enter a secured premise. The incident was documented and given to a security specialist to analyze. Which step should be taken at this stage?
#7Multiple Choice
A new malware variant is discovered hidden in pirated software that is distributed on the Internet. Executives have asked for an organizational risk assessment.
The security officer is given a list of all assets. According to NIST, which two elements are missing to calculate the risk assessment? (Choose two.)
#8Multiple Choice
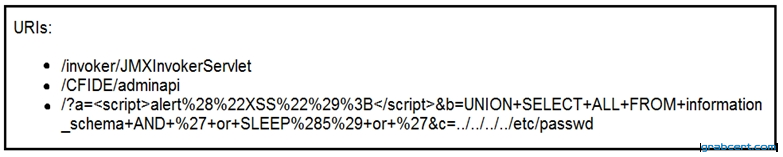
Refer to the exhibit. At which stage of the threat kill chain is an attacker, based on these URIs of inbound web requests from known malicious Internet scanners?
#9Multiple Choice
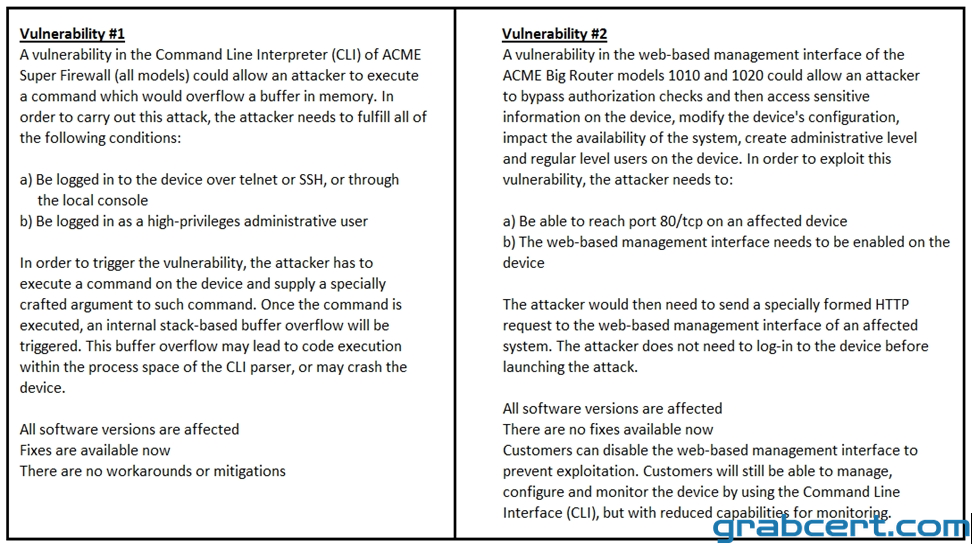
Refer to the exhibit. How must these advisories be prioritized for handling?
#10Multiple Choice
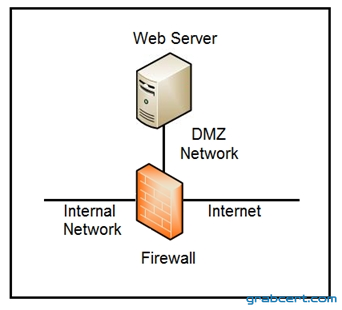
Refer to the exhibit. Which two steps mitigate attacks on the webserver from the Internet? (Choose two.)