Back to Exams
CompTIACAS-003
CompTIA Advanced Security Practitioner (CASP) CAS-003
This certification validates practical cybersecurity skills in security operations and risk control, including protecting systems, investigating threats, and applying effective controls. It is intended for professionals who assess risk and respond to real-world security scenarios.
Rate this exam
Exam Details
Total Questions
480Last Updated
Aug. 2026Rating
4.7
Question Types
Multi choices
470Drag&Drop
4Simulation
6 Get Full Access
Unlimited access to all questions
Detailed explanations for every question
Page progress: 4 / 964%
#16Multiple Choice
An organization has employed the services of an auditing firm to perform a gap assessment in preparation for an upcoming audit. As part of the gap assessment, the auditor supporting the assessment recommends the organization engage with other industry partners to share information about emerging attacks to organizations in the industry in which the organization functions. Which of the following types of information could be drawn from such participation?
#17Multiple Choice
A recent penetration test identified that a web server has a major vulnerability. The web server hosts a critical shipping application for the company and requires
99.99% availability. Attempts to fix the vulnerability would likely break the application. The shipping application is due to be replaced in the next three months.
Which of the following would BEST secure the web server until the replacement web server is ready?
#18Multiple Choice
To prepare for an upcoming audit, the Chief Information Security Officer (CISO) asks for all 1200 vulnerabilities on production servers to be remediated. The security engineer must determine which vulnerabilities represent real threats that can be exploited so resources can be prioritized to migrate the most dangerous risks. The CISO wants the security engineer to act in the same manner as would an external threat, while using vulnerability scan results to prioritize any actions.
Which of the following approaches is described?
#19Multiple Choice
An engineer is evaluating the control profile to assign to a system containing PII, financial, and proprietary data.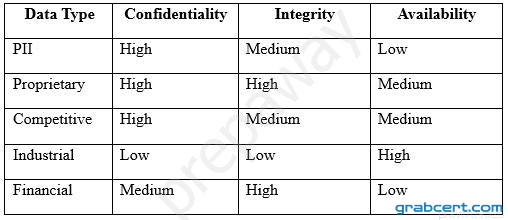
Based on the data classification table above, which of the following BEST describes the overall classification?
#20Multiple Choice
A security analyst is reviewing the corporate MDM settings and notices some disabled settings, which consequently permit users to download programs from untrusted developers and manually install them. After some conversations, it is confirmed that these settings were disabled to support the internal development of mobile applications. The security analyst is now recommending that developers and testers have a separate device profile allowing this, and that the rest of the organization's users do not have the ability to manually download and install untrusted applications. Which of the following settings should be toggled to achieve the goal? (Choose two.)