Back to Exams
CompTIACAS-005
CompTIA SecurityX
This certification validates practical cybersecurity skills in security operations and risk control, including protecting systems, investigating threats, and applying effective controls. It is intended for professionals who assess risk and respond to real-world security scenarios.
Rate this exam
Exam Details
Total Questions
475Last Updated
Aug. 2026Rating
4.7
Question Types
Multi choices
468Simulation
5Hotspot
2 Get Full Access
Unlimited access to all questions
Detailed explanations for every question
Page progress: 4 / 954%
#16Multiple Choice
Which of the following best explain why organizations prefer to utilize code that is digitally signed? (Choose two.)
#17Multiple Choice
A security engineer receives reports through the organization's bug bounty program about remote code execution in a specific component in a custom application. Management wants to properly secure the component and proactively avoid similar issues. Which of the following is the best approach to uncover additional vulnerable paths in the application?
#18Multiple Choice
A security technician is investigating a system that tracks inventory via a batch update each night. The technician is concerned that the system poses a risk to the business, as errors are occasionally generated and reported inventory appears incorrect. The following output log is provided: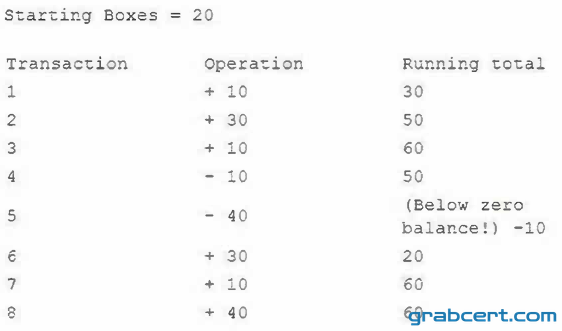
The technician reviews the output of the batch job and discovers that the inventory was never less than zero, and the final inventory was 100 rather than 60. Which of the following should the technician do to resolve this issue?
#19Multiple Choice
A programmer is reviewing the following proprietary piece of code that was identified as a vulnerability due to users being authenticated when they provide incorrect credentials: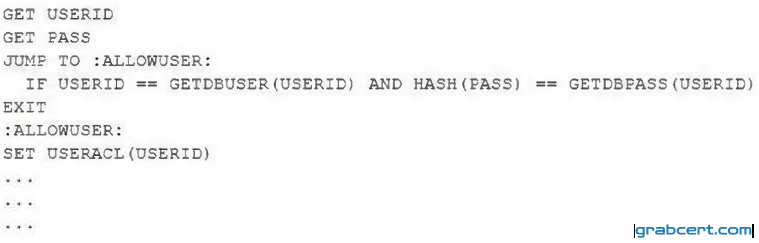
Which of the following should the programmer implement to remediate the code vulnerability?
#20Multiple Choice
A senior cybersecurity engineer is solving a digital certificate issue in which the CA denied certificate issuance due to failed subject identity validation. At which of the following steps within the PKI enrollment process would the denial have occurred?