GrabCert
HomeExamsProvidersAbout
Sign InSign Up
Home/Exams/CompTIA CompTIA CySA+ Certification Exam (CS0-002)/Question #20
#20Multiple Choice

A security analyst discovers suspicious host activity while performing monitoring activities. The analyst pulls a packet capture for the activity and sees the following:

Follow TCP stream:
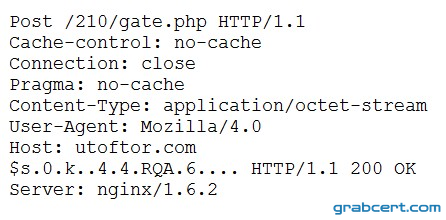
Which of the following describes what has occurred?

Previous
Question 20 of 422
Exam CS0-002 Topic 1 Question 20
Back to all questions
Next
GrabCert

Your trusted source for certification exam preparation. Pass your exams with confidence.

Quick Links

  • Home
  • Exams
  • Providers

Legal

  • About
  • Contact Us
  • Refund Policy
  • Privacy Policy
  • Terms of Service

© 2026 GrabCert. All rights reserved.

Sign InSign Up