Back to Exams
MicrosoftMS-600
Building Applications and Solutions with Microsoft 365 Core Services
This certification validates practical ability to design, deploy, and operate scalable cloud services, with emphasis on cloud architecture and operations. It is intended for professionals who manage reliable, secure, and cost-aware environments.
Rate this exam
Exam Details
Total Questions
245Last Updated
Aug. 2026Rating
4.9
Question Types
Multi choices
154Drag&Drop
23Hotspot
68 Get Full Access
Unlimited access to all questions
Detailed explanations for every question
Page progress: 2 / 494%
#6Hotspot
HOTSPOT -
You are developing an application that will run as an overnight background service on a server. The service will access web-hosted resources by using the application's identity and the OAuth 2.0 client credentials grant flow.
You register the application and grant permissions. The tenant administrator grants admin consent to the application.
You need to get the access token from Azure Active Directory (Azure AD).
Which URI should you use for the POST request? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: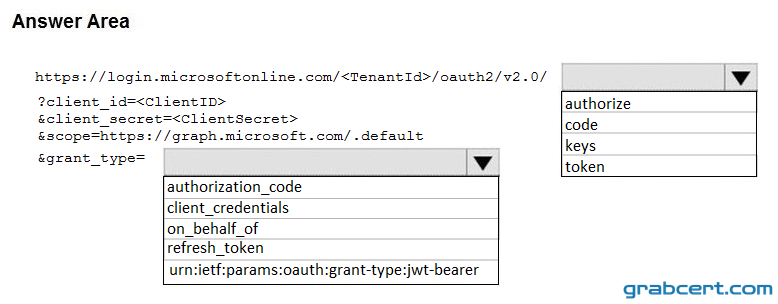
#7Multiple Choice
You develop a web API named WebApi1.
When validating a token received from a client application, WebApi1 receives a MsalUiRequiredException exception from Azure Active Directory (Azure AD).
You need to formulate the response that WebApi1 will return to the client application.
Which HTTP response should you send?
#8Multiple Choice
You have a backend service that will access the Microsoft Graph API. The backend service is hosted on-premises.
You need to configure the service to authenticate by using the most secure authentication method.
What should you configure the service to use?
#9Multiple Choice
You develop a web API named WebApi1.
When validating a token received from a client application, WebApi1 receives a MsalUiRequiredException exception from the Microsoft Identity Platform.
You need to ensure that the client application has the information required to complete the authentication.
Which header should you include in the HTTP response sent from WebApi1 to the client application?
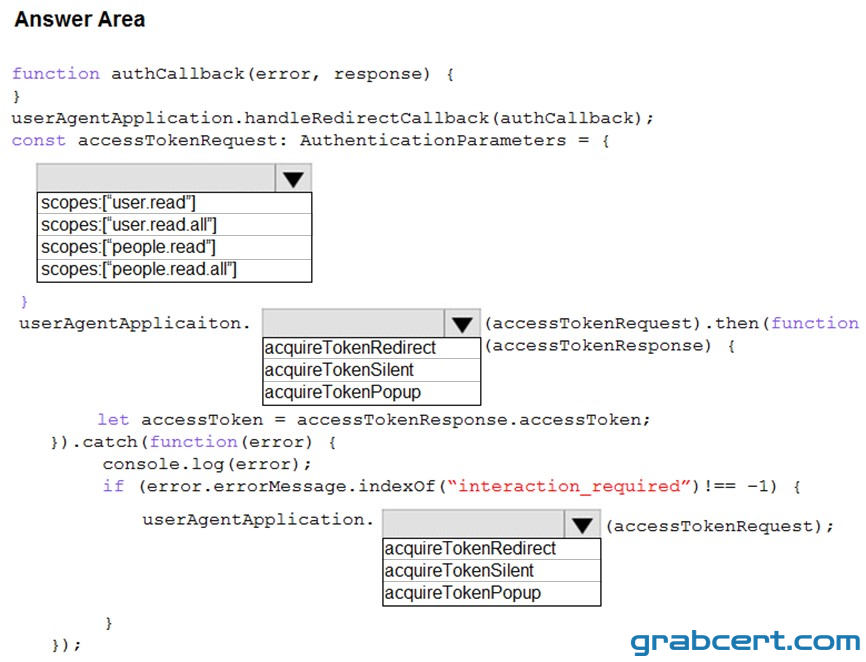
#10Hotspot
HOTSPOT -
You are developing a single-page application (SPA) named App1 that will be used by the public.
Many users of App1 restrict pop-up windows from opening in their browser.
You need to authenticate the users by using the Microsoft identity platform. The solution must meet the following requirements:
✑ Ensure that App1 can read the profile of a user.
✑ Minimize user interaction during authentication.
✑ Prevent App1 from requiring admin consent for any permissions.
How should you complete the code? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: