Back to Exams
MicrosoftSC-100
Microsoft Cybersecurity Architect
This certification validates practical cybersecurity skills in security operations and risk control, including protecting systems, investigating threats, and applying effective controls. It is intended for professionals who assess risk and respond to real-world security scenarios.
Rate this exam
Exam Details
Total Questions
340Last Updated
Aug. 2026Rating
4.8
Question Types
Multi choices
210Drag&Drop
12Hotspot
118 Get Full Access
Unlimited access to all questions
Detailed explanations for every question
Page progress: 2 / 683%
#6Multiple Choice
Your company has a Microsoft 365 subscription and uses Microsoft Defender for Identity.
You are informed about incidents that relate to compromised identities.
You need to recommend a solution to expose several accounts for attackers to exploit. When the attackers attempt to exploit the accounts, an alert must be triggered.
Which Defender for Identity feature should you include in the recommendation?
#7Multiple Choice
Your company is moving all on-premises workloads to Azure and Microsoft 365.
You need to design a security orchestration, automation, and response (SOAR) strategy in Microsoft Sentinel that meets the following requirements:
✑ Minimizes manual intervention by security operation analysts
✑ Supports triaging alerts within Microsoft Teams channels
What should you include in the strategy?
#8Multiple Choice
You have an Azure subscription that contains virtual machines, storage accounts, and Azure SQL databases.
All resources are backed up multiple times a day by using Azure Backup.
You are developing a strategy to protect against ransomware attacks.
You need to recommend which controls must be enabled to ensure that Azure Backup can be used to restore the resources in the event of a successful ransomware attack.
Which two controls should you include in the recommendation? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.
#9Hotspot
HOTSPOT -
You are creating the security recommendations for an Azure App Service web app named App1. App1 has the following specifications:
✑ Users will request access to App1 through the My Apps portal. A human resources manager will approve the requests.
✑ Users will authenticate by using Azure Active Directory (Azure AD) user accounts.
You need to recommend an access security architecture for App1.
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: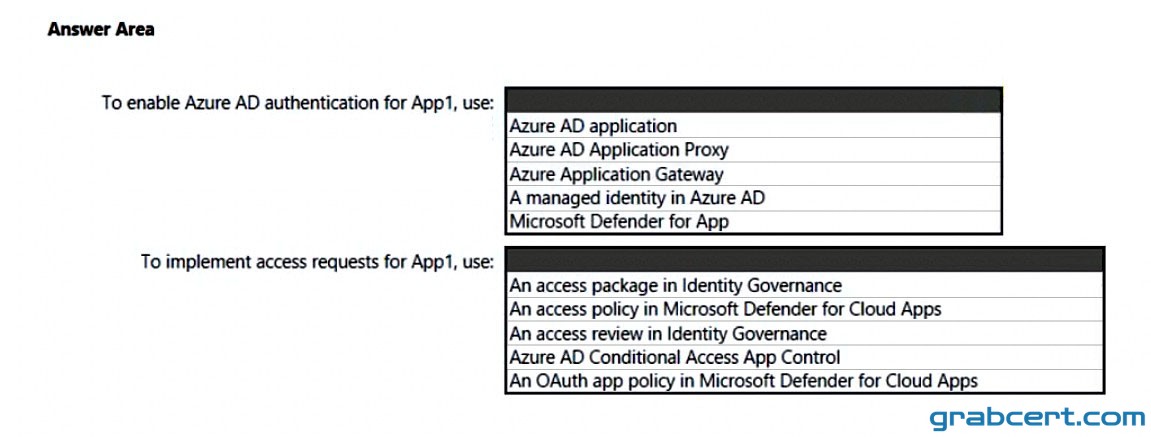
#10Hotspot
HOTSPOT -
Your company uses Microsoft Defender for Cloud and Microsoft Sentinel.
The company is designing an application that will have the architecture shown in the following exhibit.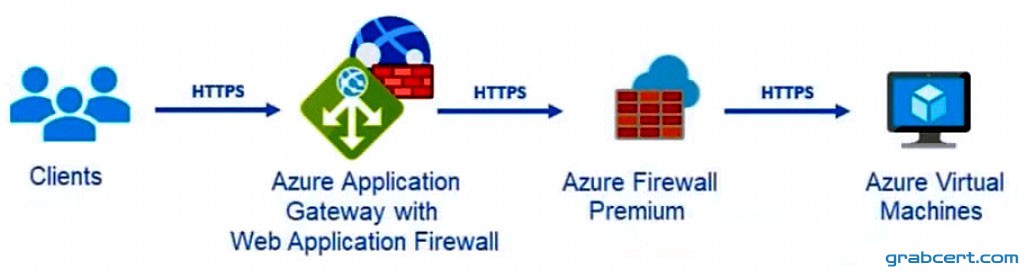
You are designing a logging and auditing solution for the proposed architecture. The solution must meet the following requirements:
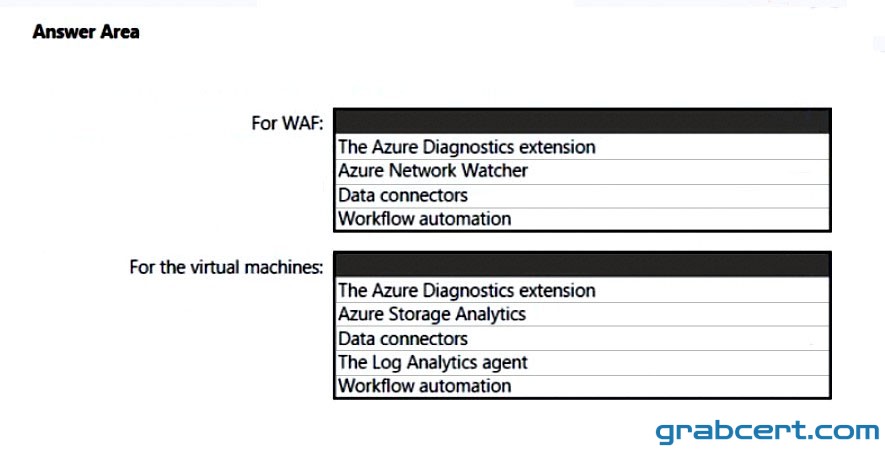
✑ Integrate Azure Web Application Firewall (WAF) logs with Microsoft Sentinel.
✑ Use Defender for Cloud to review alerts from the virtual machines.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area: