Back to Exams
Omnissa2W0_25
Omnissa Workspace ONE engineer - 2025
This certification validates practical skills in system administration and infrastructure, including deployment, administration, troubleshooting, and resilience. It is intended for professionals operating dependable enterprise technology environments.
Rate this exam
Exam Details
Total Questions
61Last Updated
Aug. 2026Rating
4.7
Question Types
Multi choices
54Drag&Drop
7 Get Full Access
Unlimited access to all questions
Detailed explanations for every question
Page progress: 1 / 138%
#1Multiple Choice
ACME has Workspace ONE UEM with Android EMM Registration at its Customer Organization Group (OG) level. The Management Mode is set to Work Managed mode for the entire organization. The sales department, which has its own container Organization Group (OG), requires switching the Work Managed mode to Corporate Owned Personally Enabled mode, without affecting the rest of the organization.
Which step should be performed to meet this requirement?
#2Multiple Choice
As part of your Workspace ONE deployment, you will be enrolling new Multiuser Windows devices for “hot seat” call center users, where users may use different devices each day.
Currently, applications deployed to these devices include common apps that are accessible to all users. A new application that installs into the HKLM registry hive must be deployed, which should only be accessible by managers, regardless of which hot seat is occupied on that day.
Which of the following deployment options should you select?
#3Drag & Drop
DRAG DROP -
An engineer must configure and deploy specific Zebra LifeGuard OTA updates for Android devices in Workspace ONE UEM.
Drag to place the following tasks in the correct order.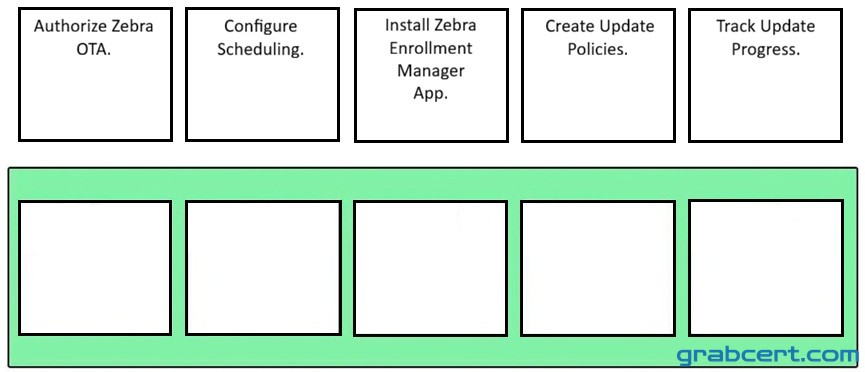
#4Multiple Choice
A workflow created in Freestyle Orchestrator to push a baseline and a custom script to macOS devices executes partially. The baseline configuration installs, but the script never executes, remaining in a Pending state. Device connectivity and smart group assignments are confirmed.
Which troubleshooting action is most appropriate?
#5Multiple Choice
You are configuring Omnissa Access for a global enterprise. The company wants to support different user groups with secure and seamless authentication:
On-premises employees should be able to log in seamlessly using existing Active Directory credentials when connected to the corporate network.
Remote employees should be able to authenticate without needing to connect to VPN, while still ensuring security and policy enforcement.
External contractors and partners should be able to use their own company’s identity provider to access Omnissa-protected applications.
Which authentication methods should you configure for each group?