Back to Exams
Oracle1Z0-897
Oracle Technology Certification
This certification validates practical skills in enterprise business systems, with emphasis on configuring processes, managing information, and supporting business outcomes. It is intended for professionals who implement or operate enterprise business systems.
Rate this exam
Exam Details
Total Questions
105Last Updated
Aug. 2026Rating
4.8
Question Types
Multi choices
105 Get Full Access
Unlimited access to all questions
Detailed explanations for every question
Page progress: 1 / 215%
#1Multiple Choice
An airline built and deployed a back-end application to manage reservations. To support interoperability with as large a base of standalone client applications as possible, the services provided by this back-end application are exposed as XML-based restful web services. Management just added a new requirement that
AJAX-based web application clients be supported, too. One of the developers suggested that it is enough to extend the existing application to support both XML- based and JSON-based restful web services. Assuming the developer is correct, choose the sentence that best describes an attempt to introduce this ability as this developer suggests (Choose one):
#2Multiple Choice
A company is refactoring an existing website to use Web services clients. The application retrieves lists of parts and displays them to the users in a browser window. Previously, the data was stored as files on the web server and, in order to access the files, the user would simply click on a hyperlink. Now the data must be dynamically generated via a service that another developer has created. They want the easiest way to refactor their website to use Web services. Which three client-side technologies should they use? (Choose three.)
#3Multiple Choice
In the code fragment below, the client will use os to upload data to the web service provider.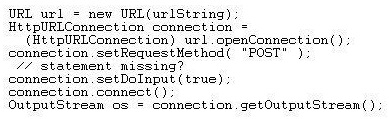
Choose the statement that must be placed in line 5, to ensure this fragment works as intended. (Choose one)
#4Multiple Choice
Given the resource class fragment: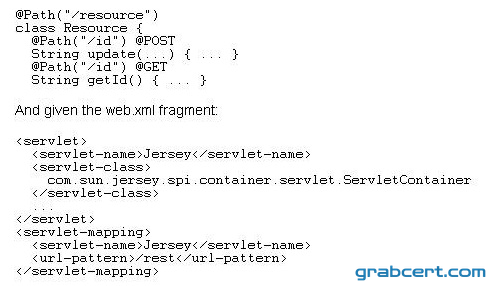
Choose the code fragment below that would secure access only to the Resource update() method (Choose one):
#5Multiple Choice
An organization has business logic implemented in EJB components. Current clients use container-managed, role-based security to access the business logic using RMI. Management has determined that the business logic must be made available to non-RMI clients using a Web service. Which container-managed Web service security mechanism would the development team?use to allow Web service clients to use the current security model? (Choose one)