Back to Exams
SalesforceCertified Platform Identity and Access Management Architect
Certified Platform Identity and Access Management Architect
This certification validates practical cybersecurity skills in identity and access management, including protecting systems, investigating threats, and applying effective controls. It is intended for professionals who assess risk and respond to real-world security scenarios.
Rate this exam
Exam Details
Total Questions
58Last Updated
Aug. 2026Rating
4.7
Question Types
Page progress: 1 / 128%
#1Multiple Choice
A financial enterprise is planning to set up a user authentication mechanism to login to the Salesforce system. Due to regulatory requirements, the CIO of the company wants user administration, including passwords and authentication requests, to be managed by an external system that is only accessible via a SOAP webservice.
Which authentication mechanism should an identity architect recommend to meet the requirements?
#2Multiple Choice
A technology enterprise is setting up an identity solution with an external vendors wellness application for its employees. The user attributes need to be returned to the wellness application in an ID token.
Which authentication mechanism should an identity architect recommend to meet the requirements?
#3Multiple Choice
Universal Containers is designing an identity architecture that involves integrating Salesforce with an external directory service. The external directory service will act as the central repository for user authentication and authorization across multiple systems within the organization.
Which approach should be evaluated to establish trust between Salesforce and the external directory service?
#4Multiple Choice
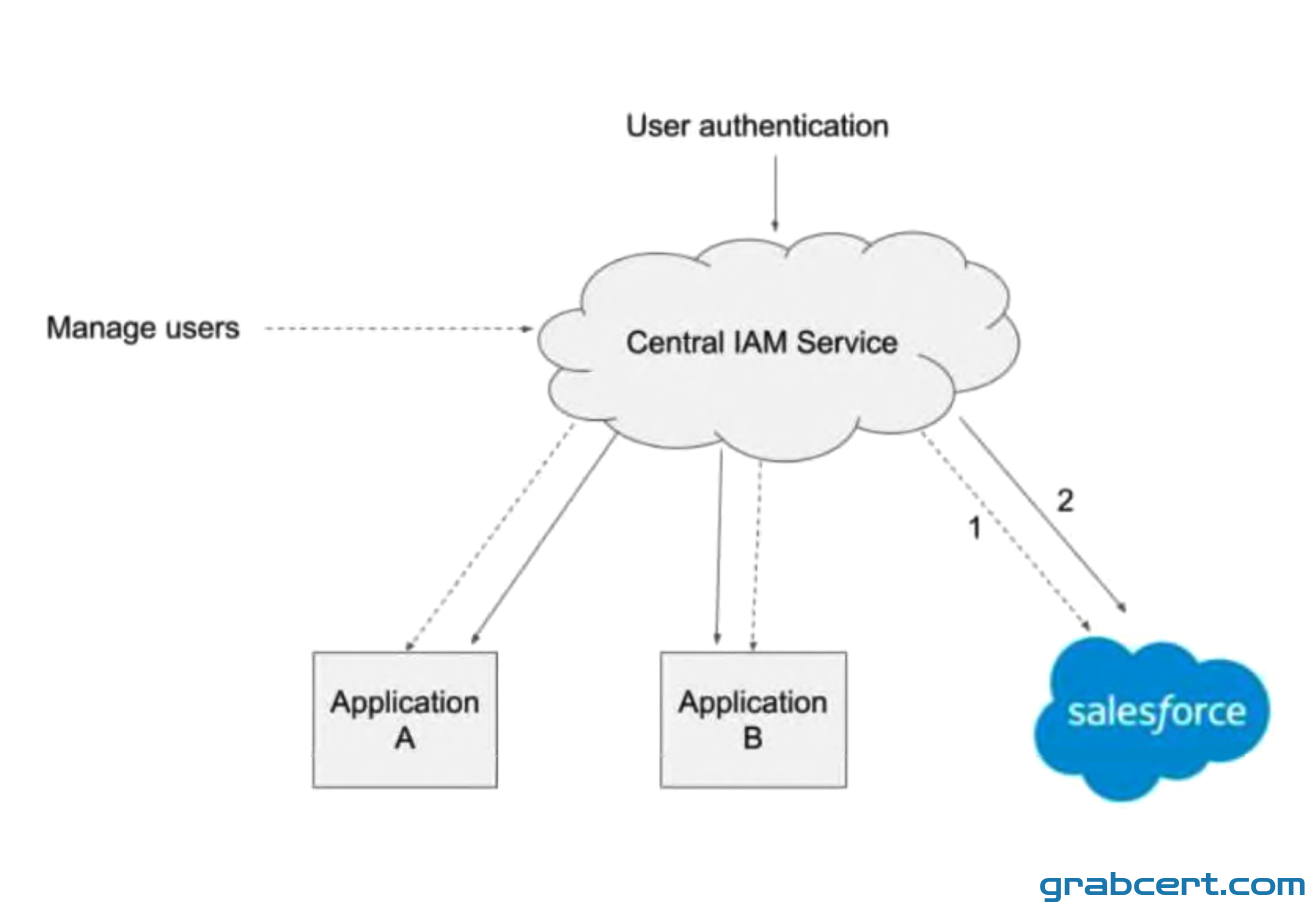
An organization has a central cloud-based Identity and Access Management (IAM) Service for authentication and user management, which must be utilized by all applications as follows:
1 - Change of a user status in the central IAM Service triggers provisioning or deprovisioning in the integrated cloud applications.
2 - Security Assertion Markup Language single sign-on (SSO) is used to facilitate access for users authenticated at identity provider (Central IAM Service).
Which approach should an IAM architect implement on Salesforce Sales Cloud to meet the requirements?
#5Multiple Choice
Universal Containers (UC) is rolling out its new Customer Identity and Access Management Solution built on top of its existing Salesforce instance. UC wants to allow customers to login using Facebook, Google, and other social sign-on providers.
How should this functionality be enabled for UC, assuming all social sign-on providers support OpenID Connect?