#3Multiple Choice
An AWS account administrator created an IAM group and applied the following managed policy to require that each individual user authenticate using multi-factor authentication: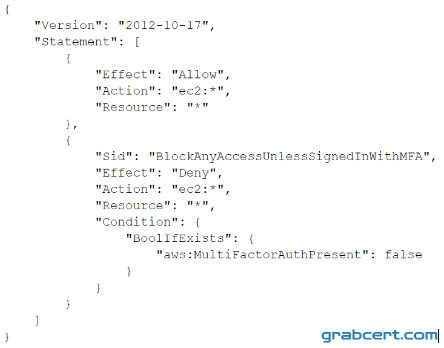
After implementing the policy, the administrator receives reports that users are unable to perform Amazon EC2 commands using the AWS CLI.
What should the administrator do to resolve this problem while still enforcing multi-factor authentication?
Question 3 of 85
Exam AWS-CERTIFIED-SECURITY---SPECIALTY-SCS-C03 Topic 1 Question 3
Back to all questions